Preparing your business for a cyber attack is one of the most commercially important decisions a UK SME owner can make. Cyber criminals do not discriminate by size. Small and medium-sized businesses are actively targeted, often because their defences are thinner and their recovery plans are weaker than those of larger organisations.
As part of Cyber Awareness Month, Wyvern Business Systems want to make sure every business we work with and every business that finds this guide, knows exactly what steps to take before an attack happens, how to respond if one does and how to recover without lasting damage.
Why SMEs Are in the Crosshairs
Many business owners assume their company is too small to be worth targeting. That assumption is one of the most dangerous positions a business can hold. Cyber criminals use automated tools that scan thousands of businesses simultaneously, looking for the easiest way in. A weak password, an unpatched system or a single employee clicking a phishing link is all it takes.
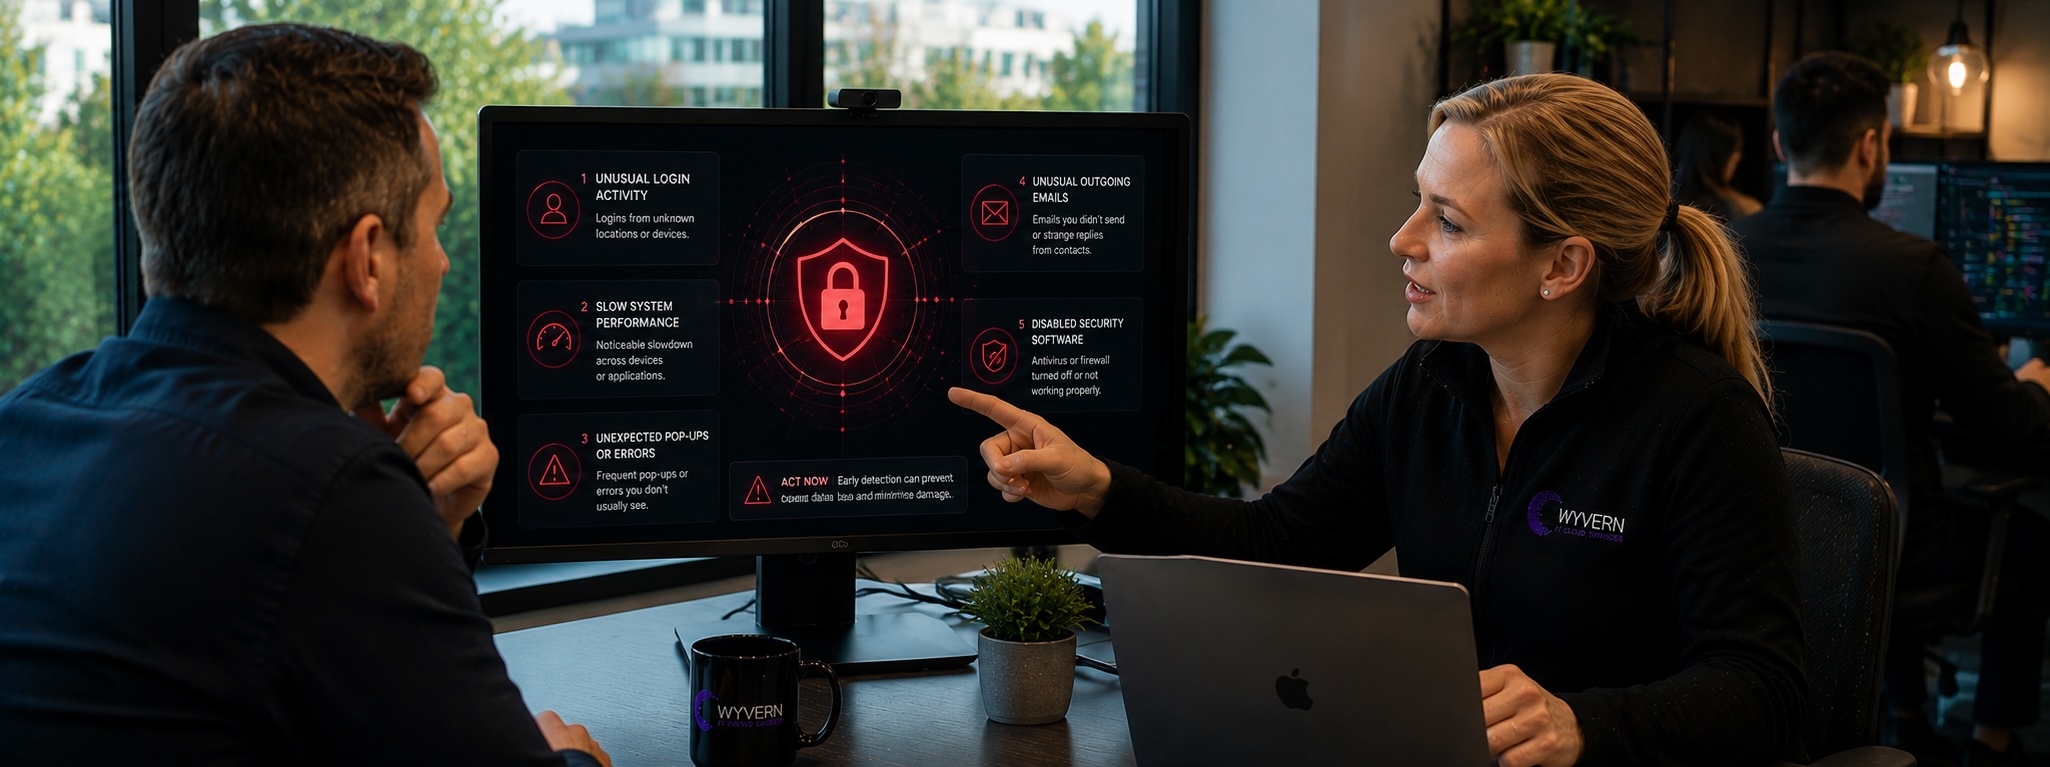
The financial consequences of a successful attack can include lost revenue, regulatory fines, reputational damage and the cost of recovery. For a small business without a contingency plan, even a short period of disruption can be deeply damaging. If you are unsure whether your business is already showing warning signs, our guide to 5 signs your SME might be under cyber attack is worth reading before you go any further.
Before, During and After: The Three Phases Every Business Must Plan For
Wyvern recently hosted a cyber security webinar built around exactly this framework. The core message was straightforward: most businesses think about cyber security only after something goes wrong. The businesses that come through attacks with minimal damage are those that planned in advance. You can watch the full cyber security webinar on the Wyvern site at no cost.
Before an Attack: Building Your Defences
The preparation phase is where most of the work happens and where most of the value is created. This is when you put the controls, training and documentation in place that will either stop an attack altogether or limit the damage if one gets through.
Strong access controls, regular patching, encrypted backups stored separately from your main systems and staff awareness training are the foundations. Without these, every other investment in technology is undermined. Getting your team to recognise a phishing email before they click it is genuinely one of the most cost-effective protective measures available.
During an Attack: Knowing What to Do When It Counts
When an attack is in progress, confusion is your biggest enemy. Every member of your team who might be involved in the response needs to know their role in advance. Who do they call first? How do you isolate an affected machine without spreading the problem? Is there a documented incident response plan they can follow?
These questions need answers before an incident occurs, not during it. The webinar covers this in detail and is freely available for any business that wants to work through the response phase properly.
After an Attack: Recovery and Lessons Learned
Recovery is about more than restoring your data. It includes communicating with clients, notifying the relevant authorities if required under UK GDPR and understanding how the attack succeeded so you can close that gap. Businesses that treat a cyber incident as a learning opportunity, rather than simply a crisis to survive, emerge meaningfully more secure.
The Importance of Cyber Essentials Certification
Cyber Essentials is a UK government-backed certification scheme that defines a clear baseline of cyber security controls. Achieving it demonstrates to clients, insurers and partners that your business takes cyber security seriously. Critically, it also forces you to address five specific technical vulnerabilities that are implicated in the vast majority of attacks.
For many SMEs, Cyber Essentials is the single most structured step they can take. Our detailed overview of Cyber Essentials certification explains what the scheme covers, who it applies to and how to work towards it. If your business does not hold this certification, that is the place to start.
Preparing Your Business for a Cyber Attack: Wyvern's Cyber Security Checklist
A checklist gives you something concrete to act on. Wyvern's SME cyber security checklist covers the key controls every business should have in place. Use it as an honest audit of where you stand today.
Top 5 Things You Can Do Right Now
These five actions do not require a large budget or a dedicated IT team. They do require a decision to act.
The first is to enable multi-factor authentication on every account that supports it. This single step blocks the majority of credential-based attacks. The second is to ensure all software, operating systems and firmware are kept up to date, since unpatched vulnerabilities are among the most common entry points attackers use.
The third is to run a simulated phishing test with your team. Understanding who is likely to click before a real attack arrives is far more valuable than finding out after one. The fourth is to verify your backup process, not just that backups exist but that they are tested, recent and stored separately from your live environment. The fifth is to document your incident response plan, even a single page that covers who is responsible for what, so your team is not starting from scratch in a crisis.
How Wyvern Can Help
Wyvern's managed IT services are built around proactive protection, not reactive firefighting. The team works with SMEs across Herefordshire and beyond to put the right controls in place, maintain them consistently and respond quickly when something needs attention.
That kind of proactive monitoring is exactly what cyber security requires. If you would like to explore how Wyvern can support your business, you can book a no-obligation call with the team to talk through your current position and where the gaps might be. There is no pressure and no sales script, just a practical conversation about where your business stands.
You can also visit the events and webinars page to access the free cyber security webinar and any upcoming sessions that might be relevant to your business.
Frequently Asked Questions
What is the first thing a business should do to prepare for a cyber attack?
Start with an honest audit of your current controls. Multi-factor authentication, up-to-date software and a tested backup process are the three foundations. If any of these are missing, address them before anything else.
Does Cyber Essentials certification actually make a difference for small businesses?
Yes. The certification requires you to meet five specific technical controls that close the vulnerabilities most commonly exploited in attacks. It also signals to clients and insurers that your business has taken a structured approach to security.
What should I do if my business is currently under a cyber attack?
Isolate the affected devices from your network immediately and contact your IT support provider. Do not attempt to investigate the attack yourself without guidance, since poorly managed responses can spread the damage. Have your incident response plan to hand, even if it is a basic one.
How often should a business review its cyber security?
At a minimum, review your controls annually and whenever there is a significant change to your systems, team or suppliers. Cyber threats evolve quickly, so a point-in-time review is not sufficient on its own., Preparing your business for a cyber attack takes time, focus and the right support, but the cost of preparation is a fraction of the cost of a successful breach. Start with the checklist, watch the free webinar and speak to Wyvern about what a properly managed, proactive approach to cyber security looks like for a business your size. Contact Wyvern today to arrange your no-obligation conversation.
No Comments Yet
Let us know what you think